UK GDPR Compliance for Conversational AI: The 2026 Contact Centre Checklist
Since the Data (Use and Access) Act 2025 took full effect in February 2026, the stakes for data protection have reached a new peak. A single oversight in your automated workflows can now trigger fines of up to £17.5 million or 4% of your global turnover. It's a sobering reality for enterprise leaders. You understand that achieving gdpr compliance for conversational ai uk is no longer a peripheral legal concern. It's a core architectural requirement. You want the efficiency of advanced automation, yet the complexity of managing PII within unstructured AI conversations remains a significant source of anxiety.
We believe that privacy shouldn't be the enemy of performance. This article provides a definitive roadmap to master UK data protection while deploying sophisticated conversational agents in your contact centre. You'll learn how to navigate the ICO's latest statutory codes and implement privacy-by-design that actually works. We're moving beyond legacy limitations to build a future where every customer interaction is both intelligent and inherently secure. By the end of this checklist, you'll have the clarity needed to integrate AI with existing regulatory frameworks without compromising your brand reputation.
Key Takeaways
- Navigate the transition to the Data (Use and Access) Act 2025 to safeguard your enterprise against the new £17.5 million fine threshold.
- Master gdpr compliance for conversational ai uk by implementing real-time PII masking and robust prompt shields within your automated workflows.
- Adopt a Privacy-by-Design architecture using Hybrid RAG to ensure absolute process accuracy while maintaining strict data sovereignty.
- Audit AI vendor transparency and model training policies to guarantee that sensitive customer data is never shared with external third parties.
- Establish sophisticated governance for agentic swarms that balances seamless session continuity with the highest standards of interpersonal privacy.
Navigating the UK Data Privacy Landscape in 2026
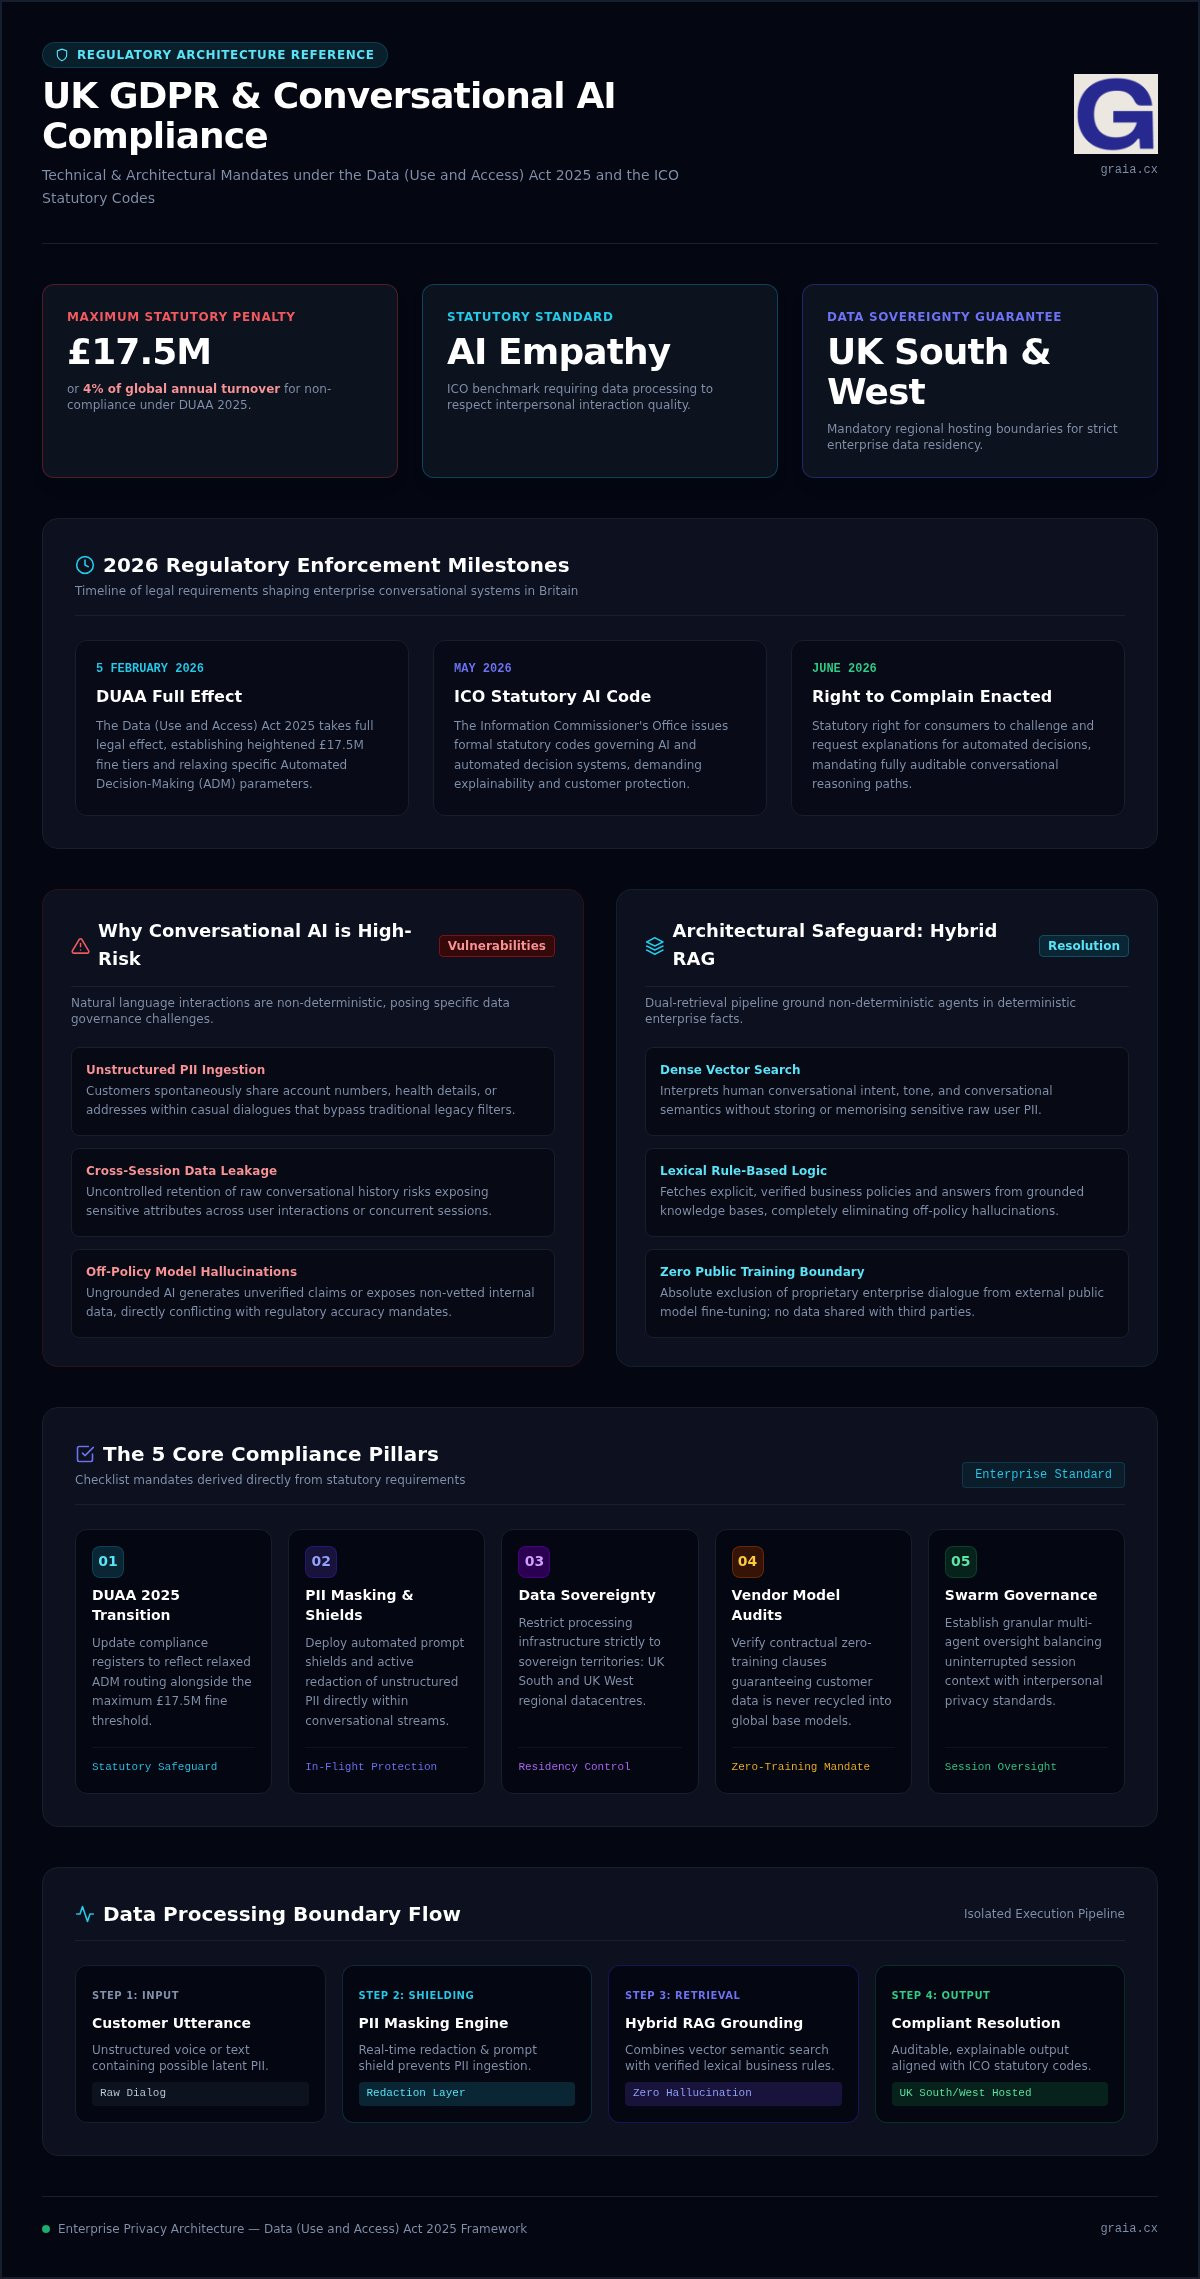
The digital frontier has shifted. On 5 February 2026, the Data (Use and Access) Act 2025 (DUAA) fundamentally altered the regulatory terrain for every enterprise contact centre in Britain. While the core principles of the General Data Protection Regulation (GDPR) remain the bedrock of privacy, the UK has pivoted toward a framework that balances rigorous protection with industrial agility. This evolution demands a new level of technical sophistication from Data Protection Officers. Achieving gdpr compliance for conversational ai uk requires more than just ticking boxes; it necessitates a deep understanding of how non-deterministic models interact with sensitive human intent.
The Information Commissioner's Office (ICO) now operates with enhanced clarity following the May 2026 statutory code on AI and automated decision-making. They expect organisations to demonstrate not just technical safety, but 'AI Empathy'-a standard where data processing respects the interpersonal quality of the customer experience. Compliance is no longer a static state. It's a continuous, intelligent process of protecting the human element within a digital framework.
The Impact of the Data (Use and Access) Act 2025
The DUAA represents the most significant update to British data law since Brexit. It streamlines data processing for AI research, allowing firms to innovate with fewer administrative hurdles. However, the stakes for mismanagement are higher than ever. Fines now align with the most stringent tiers, reaching up to £17.5 million or 4% of global turnover. For contact centres, the most critical shift involves Automated Decision-Making (ADM). The previous broad prohibition has been relaxed, giving you more flexibility to use AI for recruitment or service routing, provided that safeguards for special category data remain absolute. You must ensure your systems can explain every decision to a customer who exercises their new statutory right to complain, effective since June 2026.
Why Conversational AI is a High-Risk Category
Conversational agents process natural language, which is inherently messy. Customers often share 'unstructured PII'-account numbers, health details, or addresses-in the middle of a casual sentence. Traditional legacy systems aren't built to catch these fragments in real-time. When an AI lacks proper grounding, it risks 'hallucinating' or leaking sensitive data across sessions. Securing gdpr compliance for conversational ai uk involves architecting systems that recognise the nuance of human speech without retaining the risk of its exposure. You must ground your agents in factual, vetted knowledge bases. This prevents the model from generating off-policy responses that could lead to a catastrophic breach of trust or a direct regulatory intervention.
Architectural Integrity: Privacy-by-Design in Agentic RAG
Architectural integrity isn't a luxury. It's the foundation of trust. For enterprises deploying advanced agents, the shift to agentic Retrieval-Augmented Generation (RAG) offers a unique path to security. Unlike generic models that ingest and regurgitate data indiscriminately, a privacy-first execution engine isolates sensitive information at the source. This architecture ensures that your specific customer data remains within your control, residing exclusively in regional hosting environments like UK South or UK West. Maintaining data sovereignty is non-negotiable for ICO's Guidance on AI and data protection, which demands that organisations maintain clear boundaries over how personal data is processed.
A critical differentiator in modern systems is the absolute exclusion of client data from public model training. Your interactions shouldn't become the fuel for a competitor's AI. By ensuring that data is never shared or used to train external models, you eliminate the risk of PII leakage into the global digital commons. This level of technical isolation is essential for achieving gdpr compliance for conversational ai uk in high-stakes environments. It ensures that your commitment to privacy is woven into the very fabric of your technology stack rather than being a mere policy afterthought.
Hybrid RAG: Grounding AI in Facts
Hallucinations are a compliance nightmare. To prevent the processing of false data, we utilise Hybrid RAG, which combines dense vector search with business-critical, rule-based logic. While vector search handles the nuance of human intent, lexical search ensures that specific, vetted facts are retrieved with 100% accuracy. This dual-layered approach is vital for regulated sectors like finance or travel, where a single incorrect response regarding a refund or a policy can lead to regulatory friction. It replaces the 'black box' of standard AI with a transparent, grounded framework that supports gdpr compliance for conversational ai uk by ensuring data accuracy.
Encryption and Data Isolation
Security must exist at every layer. We employ TLS 1.2 for all data in transit and AES256 for data at rest, creating a robust shield around customer PII. However, encryption alone isn't enough. True privacy requires software orchestration that ensures total tenant isolation. Multi-tenancy must be managed with precision so that data from one organisation never touches another. On the human side, Role-Based Access Control (RBAC) and Multi-Factor Authentication (MFA) ensure that only authorised supervisors can access sensitive logs. You can explore more about building secure AI architectures to see these principles in action.
The 2026 Conversational AI Compliance Checklist
Efficiency is the goal; compliance is the guardrail. Achieving gdpr compliance for conversational ai uk requires moving beyond static documentation into active, technical enforcement. It's about building a system that protects the human at every turn. You need a rigorous protocol to vet your technology partners and your internal workflows. This checklist serves as your operational blueprint, ensuring that your deployment isn't just fast, but fundamentally safe.
Before launching any new automated workflow, you must verify that your infrastructure can handle the nuance of the Data (Use and Access) Act 2025. This includes configuring automated testing to identify model hallucinations before they ever reach a customer. If an agent provides incorrect advice on a regulated financial product, the liability rests with you. Continuous monitoring through 'Conversational Agent Insights' provides the transparency required to prove that your safeguards are functioning as intended.
The Essential Technical Audit
Your relationship with your AI vendor is your first line of defence. You must demand absolute clarity on their data training policies. Does the vendor use your proprietary customer interactions to train their base models? For many, the answer is a quiet 'yes', which creates an unacceptable risk of data leakage. A compliant partner ensures that your data is never shared or used for external training. You also need to confirm that 'Prompt Shields' are active. These shields prevent injection attacks where a user might attempt to trick the AI into bypassing security protocols or revealing sensitive system information. Finally, ensure there's a transparent audit trail for every reasoning step the AI takes, allowing your DPO to reconstruct any interaction during a regulatory review.
Operational Compliance Requirements
Operational safety is built at the node level. When designing your agent's logic, use 'Decision' nodes to maintain structured, compliant routing for sensitive requests. This ensures that high-risk queries are always handled according to your specific policy. For data intake, implement 'Collect Data' nodes equipped with regex validation. This technical layer prevents the agent from accepting or storing PII that doesn't match a required format, such as a postcode or an account number, effectively filtering out 'unstructured' risk before it enters your database. Mandatory disclosures must also be script-locked. By providing agents with locked suggestions for legal disclaimers, you ensure that every regulatory requirement is delivered verbatim, protecting both your brand reputation and your legal standing in the UK market.
Governance of the AI Swarm: Transparency and Oversight
Complexity scales with intelligence. As your contact centre evolves from monolithic chatbots to an agentic swarm, the governance of data handoffs becomes your most critical vulnerability. You aren't just managing one conversation; you're orchestrating a network of specialised agents. A Billing Agent and a Technical Support Agent require different data sets to function. Over-sharing PII between these nodes violates the principle of data minimisation, a core pillar of gdpr compliance for conversational ai uk. You need a system that enforces 'least privilege' access across the entire ecosystem.
To maintain oversight, we deploy AI 'Judges'-secondary models that score every interaction for policy adherence in real-time. These judges act as an automated compliance department, identifying deviations before they escalate into breaches. This layer of transparency ensures that your automation remains protective rather than predatory. It provides the evidence-based reasoning required to satisfy the ICO's demand for accountability in automated systems.
Managing Multi-Agent Ecosystems
The 'Intelligent Routing Brain' serves as the central nervous system of your swarm. It preserves the customer's intent while strictly limiting data exposure to the specific agent in play. If a customer moves from a billing query to a technical issue, the system transfers the context without exposing unnecessary financial details. This granular control is essential for maintaining audit-ready transcripts, particularly in multilingual calls where live translation must also adhere to strict privacy rules. You can explore our guide to agentic governance to see how this architecture prevents data sprawl.
The Seamless Human Handoff
Technology should elevate the human potential, not replace it. When an interaction requires a 'human-in-the-loop', the handoff must be seamless and secure. By providing live agents with structured, PII-masked summaries, you eliminate the 'repeat yourself' frustration that plagues modern CX. This approach respects the customer's time and their privacy. Real-time coaching and sentiment analysis further empower your staff, ensuring that human oversight is technically supported and emotionally intelligent. It's about creating a partnership where the AI handles the data and the human handles the connection, ensuring that gdpr compliance for conversational ai uk is maintained even when the machine steps aside.
Securing the Future with GraiaCX's Privacy-First AI
The legacy of the past shouldn't anchor your future. As enterprise leaders, you face the dual pressure of driving efficiency while shielding your organisation from regulatory volatility. GraiaCX's Buzzeasy platform, built on the robust foundation of Microsoft Azure, is designed specifically for this high-stakes environment. We leverage 25 years of CX industry innovation to ensure that your pursuit of contact centre ROI with AI never comes at the expense of customer trust. By prioritising data sovereignty and technical transparency, we provide a stable, reassuring presence that allows your enterprise to evolve with confidence. Achieving gdpr compliance for conversational ai uk is a complex endeavour, but it becomes a strategic advantage when your technology stack is inherently protective.
Our commitment to privacy is absolute. We ensure that your sensitive data is never shared or used to train external models, maintaining a strict boundary between your intellectual property and the global digital commons. This architectural integrity is what allows us to deliver empathetic, accurate automation that resonates with the human experience. We don't just process data; we elevate the interpersonal connection through intelligence that respects every individual's right to privacy.
Integration Without Compromise
Modernising a contact centre shouldn't require a total overhaul of your existing infrastructure. GraiaCX provides native support for enterprise ai contact center standards, allowing you to connect advanced agents to legacy systems like Avaya, Genesys, and NICE CX. Through secure, encrypted APIs, we bridge the gap between your established CRM or ERP systems and the future of agentic CX. This no-code approach enables day-1 automation, ensuring that your transition to a more intelligent service model is seamless. You can modernise your operations without compromising the security protocols that your organisation has spent years perfecting, maintaining gdpr compliance for conversational ai uk across every touchpoint.
The Path Forward for UK Enterprises
In 2026, the adoption of a sophisticated agentic ccaas platform is no longer optional for those who wish to remain competitive in the British market. The urgency for evolution is real, yet it must be tempered by practical results. We invite you to stress-test your current compliance workflows by requesting a simulator test. This allows you to see how our PII masking, prompt shields, and hybrid RAG work in a controlled environment before full deployment. The goal is clear: trustworthy automation that protects your brand and empowers your people. Explore our latest insights on AI compliance to start your journey toward a more secure, intelligent future today.
Mastering the Future of Compliant Automation
The evolution of the UK regulatory landscape represents a fundamental shift from reactive compliance to proactive architectural integrity. You've seen how grounding your automation in Hybrid RAG and implementing real-time PII masking can transform a source of anxiety into a definitive competitive differentiator. Achieving gdpr compliance for conversational ai uk is the essential bridge between technical excellence and lasting customer loyalty. We believe that every interaction is an opportunity to build trust through transparency. This journey toward compliant AI isn't just about avoiding fines; it's about fostering a digital environment where your customers feel truly safe and understood.
GraiaCX's architecture is built on the Microsoft Azure Trust Framework, ensuring your data sovereignty is never compromised. With PII masking and prompt shields included as standard, our ISO and SOC2 aligned platform provides the reassuring stability your enterprise requires. You don't have to choose between advanced intelligence and absolute safety. It's time to lead with vision and protect with precision. Secure your contact centre's future-read our latest AI compliance guides. We're here to ensure your operations remain resilient, empathetic, and fully compliant in 2026 and beyond.
Frequently Asked Questions
Is my customer data used to train GraiaCX's AI models?
GraiaCX guarantees that your customer data is never used to train our base models or any third-party AI. This technical boundary prevents PII from entering the global digital commons. By ensuring that your interactions remain within your specific tenant, we uphold the highest standards of gdpr compliance for conversational ai uk. This isolation strategy is critical for enterprises that require absolute data sovereignty without sacrificing the power of large language models.
How does the Data (Use and Access) Act 2025 affect my contact centre?
The Data (Use and Access) Act 2025 streamlines AI research while introducing a new statutory right for individuals to complain directly to data controllers. Effective since June 2026, this shift requires you to have formal internal resolution processes in place. Furthermore, while automated decision-making rules have been relaxed, the potential for £17.5 million fines means your AI guardrails must be more robust than ever to ensure continuous policy adherence.
What are 'Prompt Shields' and why are they necessary for GDPR?
Prompt shields are proactive security layers designed to block malicious injection attacks and prevent the AI from generating off-policy content. They're necessary for GDPR because they act as a real-time firewall against data exfiltration attempts and toxicity. By preventing users from 'jailbreaking' the agent's logic, these shields ensure that your automated interactions remain within the bounds of lawfulness, fairness, and transparency as mandated by the ICO.
Can conversational AI handle PII masking in real-time?
Modern conversational agents can identify and redact sensitive information like account numbers or health details in real-time during voice and chat interactions. This capability, which is a core feature of the GraiaCX platform, prevents unstructured PII from being stored in logs or processed by the LLM. It ensures that your data protection strategy is active rather than reactive, providing a technical solution to the common fear of accidental data breaches in natural language.
How do I ensure 100% process accuracy with an AI agent?
Achieving 100% process accuracy requires the use of Hybrid Flows, which anchor AI natural language understanding in deterministic, rule-based logic. This ensures that mission-critical tasks, such as processing a financial transaction, follow your exact business protocols without deviation. By combining the flexibility of an LLM with the rigidity of a decision tree, you eliminate the risk of the agent going off-policy, which is vital for maintaining gdpr compliance for conversational ai uk.
What happens if the AI fails or hallucinates during a customer call?
If an AI agent reaches the limit of its knowledge or begins to hallucinate, the system initiates a seamless human handoff. The live agent receives a structured summary of the interaction, including the context and intent, so the customer doesn't have to repeat themselves. This human-in-the-loop oversight ensures that complex or high-risk escalations are always handled with empathy and accuracy, maintaining the integrity of the customer journey at all times.
Does GraiaCX support UK-based data hosting for compliance?
GraiaCX fully supports UK-based data hosting through Microsoft Azure's regional data centres. This allows you to host all personal data within the UK jurisdiction, satisfying the requirements for data sovereignty and regional adequacy. By keeping your data within these borders, you simplify your compliance architecture and align with the ICO's latest guidance on AI and data protection, ensuring your enterprise remains protected against international data transfer risks.
How does real-time translation maintain GDPR compliance?
Real-time translation maintains compliance by using secure APIs and providing script-locked suggestions to ensure mandatory disclosures are delivered verbatim. Unlike consumer apps, our enterprise solution does not store or share the audio for external model training. It generates audit-ready transcripts for every multilingual interaction, allowing you to resolve disputes and prove adherence to UK regulatory frameworks while serving a global audience in over 100 languages and dialects.